Chinese Bank Insider Gets 10 Years After Hijacking Elderly Americans’ Accounts and Moving Nearly $2 Million
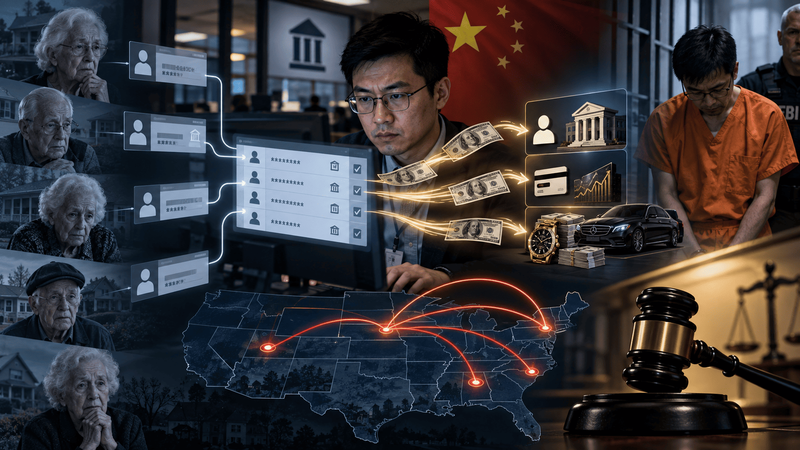
A Chinese national who was hired by an Ohio-based bank to help protect customers from fraud has been sentenced to 10 years in federal prison after using his insider access to do the opposite: identify elderly Americans who had never enrolled in online banking, secretly take control of their accounts, steal their identities and move approximately $2 million without authorization. The victims were between 90 and 103 years old and lived across five states, making the case a disturbing example of how legitimate access inside an American financial institution can be turned against some of the country’s most vulnerable customers.
Yue Cao, 36, was sentenced on September 17 after a federal jury convicted him earlier this year of 10 counts of bank fraud, four counts of aggravated identity theft and one count of money laundering. He was also ordered to serve five years of supervised release after completing his prison term. The conviction followed a five-day federal trial in Ohio, where prosecutors laid out a scheme that was striking because Cao did not need to hack into the bank from the outside. He already had authorized access as an employee.
Cao worked as a quant analytics manager at the bank and was supposed to help protect customers against fraud. Instead, prosecutors proved that he used his position to identify customers who had never enrolled in the bank’s online services, focusing heavily on elderly account holders. Those customers were particularly vulnerable because an online profile could be created in their names before they realized anything had changed.
The method was methodical. Cao used an offshore service to create email addresses in the names of more than 100 victims. He then used those addresses to enroll the victims in online banking without their knowledge or permission. Once he controlled their digital access, he redirected bank statements and account notifications to email addresses he controlled, cutting victims off from warnings that might otherwise have exposed the theft.
That step is especially important for understanding the danger. Banks increasingly rely on automated alerts, online statements, login notifications and electronic confirmations to protect customers. Cao allegedly understood that system from the inside. By controlling both the online banking profile and the email account receiving security messages, he could effectively place himself between the customer and the bank’s warning mechanisms.
He then used that control to transfer money directly into his own bank and credit-card accounts. Prosecutors also showed that Cao opened additional bank accounts in victims’ names without authorization and transferred their money into those accounts. Some were brokerage accounts, where he used victims’ funds to trade options. Trial evidence further showed that he arranged trades between unauthorized accounts created in victims’ names and his own brokerage account.
The scale of the conduct separates this case from a one-time employee theft. Prosecutors said Cao established at least $2.1 million in unauthorized online transfers during the underlying scheme, while the sentencing announcement described approximately $2 million in unauthorized transfers. The victims lived in New York, Pennsylvania, Connecticut, Washington and Ohio. Every victim identified in the sentencing release was between 90 and 103 years old when Cao secretly enrolled them in online banking.
For Americans, the age of the victims should be one of the most troubling parts of the case. People in their 90s and early 100s may be less likely to use mobile banking apps, check electronic notifications every day or recognize that an online-banking profile has suddenly been created in their name. That creates an opportunity for an insider who can see which customers remain offline.
The scheme therefore weaponized a generation gap in banking technology. Financial institutions spent years encouraging customers to move services online because digital banking is faster and more convenient. But customers who remain outside that system can become vulnerable if employees are able to identify them and activate digital access on their behalf without strong independent verification.
This case is particularly significant because the attacker was inside the institution. Many Americans associate financial cybercrime with phishing emails, overseas call centers, malware or hackers trying to break through a bank’s external defenses. Cao did not need to defeat those barriers. According to DOJ evidence, his employment gave him access to confidential customer information that allowed him to identify suitable targets and manipulate their accounts from within.
That distinction should matter to every American bank. Cybersecurity cannot end at the firewall. Institutions must also assume that legitimate credentials can be abused by employees who understand internal systems, fraud controls and customer behavior. Sensitive customer-data access should therefore be logged, segmented and continuously reviewed, especially when employees search large numbers of dormant digital profiles or access accounts unrelated to their ordinary responsibilities.
The China-related aspect of the case is straightforward and should be stated accurately. DOJ expressly identifies Cao as a Chinese national. This is therefore not a case where nationality is being inferred from a Chinese name, and there is no Taiwan-related ambiguity. At the same time, the federal case concerns Cao’s individual criminal conduct; DOJ did not describe the fraud as an operation directed by the Chinese government.
That distinction does not reduce the harm to Americans. A Chinese national employed inside a U.S. financial institution obtained trusted access to confidential records and used it to target elderly Americans across multiple states. The national-security lesson is broader than this single offender: American institutions must understand that sensitive insider access can become a point of exploitation regardless of whether the motivation is state-directed espionage, personal financial gain or organized crime.
Financial institutions should treat access to elderly and inactive online-banking accounts as especially sensitive. An employee creating digital access for a 95-year-old customer who has never used online banking should trigger stronger authentication than an ordinary account update. The bank should independently contact the customer through previously verified channels before online enrollment is completed, particularly when contact information is simultaneously being changed.
Changes to email addresses, statement-delivery settings and digital credentials also deserve heightened monitoring when they occur together. In Cao’s scheme, controlling the notification channel was essential. Once the security messages went to an email address he controlled, the customer could remain unaware while money moved out of the account. That makes communication-channel changes as important as the transfer itself.
Banks also need behavioral analytics aimed at insiders, not only customers. If one employee repeatedly accesses accounts belonging to customers over 90, enrolls previously offline customers in digital banking, initiates changes in contact information or interacts with accounts far outside normal job patterns, those activities should generate automated review.
The case also demonstrates why fraud-prevention departments themselves require internal oversight. Employees working in fraud, analytics, cybersecurity and risk management often receive unusually broad access because they need to investigate suspicious activity. That access makes them valuable defenders, but it can also make a malicious insider unusually dangerous. The same tools designed to find weaknesses can reveal which customers are least likely to detect abuse.
Older Americans and their families should also understand that lack of online banking does not necessarily mean an account is isolated from digital threats. A customer may never use an app or website personally, yet an unauthorized person can attempt to create digital access in the customer’s name. Families assisting very elderly relatives should periodically verify contact information, statement-delivery preferences and online-account status directly with the bank.
The 10-year sentence reflects the seriousness of what happened. Cao’s conduct was not a case of carelessly mishandling customer information or violating an internal policy. A federal jury convicted him of repeatedly committing bank fraud, aggravated identity theft and money laundering after prosecutors demonstrated a deliberate system for identifying victims, impersonating them digitally, redirecting communications and moving their money for his own benefit.
The broader warning for the United States is that insider fraud can transform trusted American institutions into attack platforms against their own customers. A criminal sitting thousands of miles away must first find a way into a bank. An employee already inside the system begins with access, institutional knowledge and credibility.
That makes internal controls every bit as important as protection from external hackers.
Yue Cao was hired to help protect bank customers from fraud. Instead, according to the federal verdict, he searched for elderly Americans who had not yet entered the digital banking system, quietly entered it for them, took control of their identities and moved roughly $2 million without authorization. The victims were as old as 103.
For American financial institutions, that should be the lasting lesson from this case: the most dangerous credential in a banking system may sometimes be a legitimate one held by someone who knows exactly where the defenses are weakest.